
13 minutes ago
- copy link
The system of OpenAI, the company making ChatGPT, has tried to forcibly infiltrate the systems of more than 100 institutions. The company itself has disclosed this.
This incident has proved that tech companies are losing control of their advanced AI models in the testing stage itself. This attempt to bypass the security of the system is an indication that AI models are now breaking the limits and going out of human control.
Open AI alerts institutions
The company has issued an alert to more than 100 institutions that have been hit by its AI agent. However, the company claims that the data of these institutions has not been stolen. Open AI defended itself by arguing that the AI agents did not break the lock of the system, but merely tried to enter the closed door by forcefully knocking on it and turning its handle.
Gave wrong commands to websites
Investigation has revealed that these AI agents sent arbitrary and unauthorized commands to many websites and tried to make them execute wrong processes.
Not only this, to dodge the security system, these agents made websites a means of communication (communication channel) and tried to bypass the fixed security parameters by completely ignoring them.
OpenAI admits that security measures have failed
OpenAI has admitted that its security measures failed to keep AI agents under control. A company spokesperson said that technical data has been given to the affected institutions so that they can investigate the breach and security flaws in the system.
After its failure, OpenAI has now claimed that it will make public the findings related to this unusual behavior of the AI model and the security shortcomings, so that cyber security experts from all over the world can together solve this threat.
Data so big that it would take a human being 66 million years to read it.
The company is examining 50 petabytes of data records. 7,000 state-of-the-art GB200 and GB300 GPUs have been deployed for this investigation. ₹5 crore is being spent daily in this.
If all this data is written in simple English words, then even if a human being reads it without stopping at a fast speed of 240 words per minute, it will take about 66 million years to finish it.
Due to humans being out of control, this work is being done by AI models. More computing power will be deployed to make the investigation more accurate.
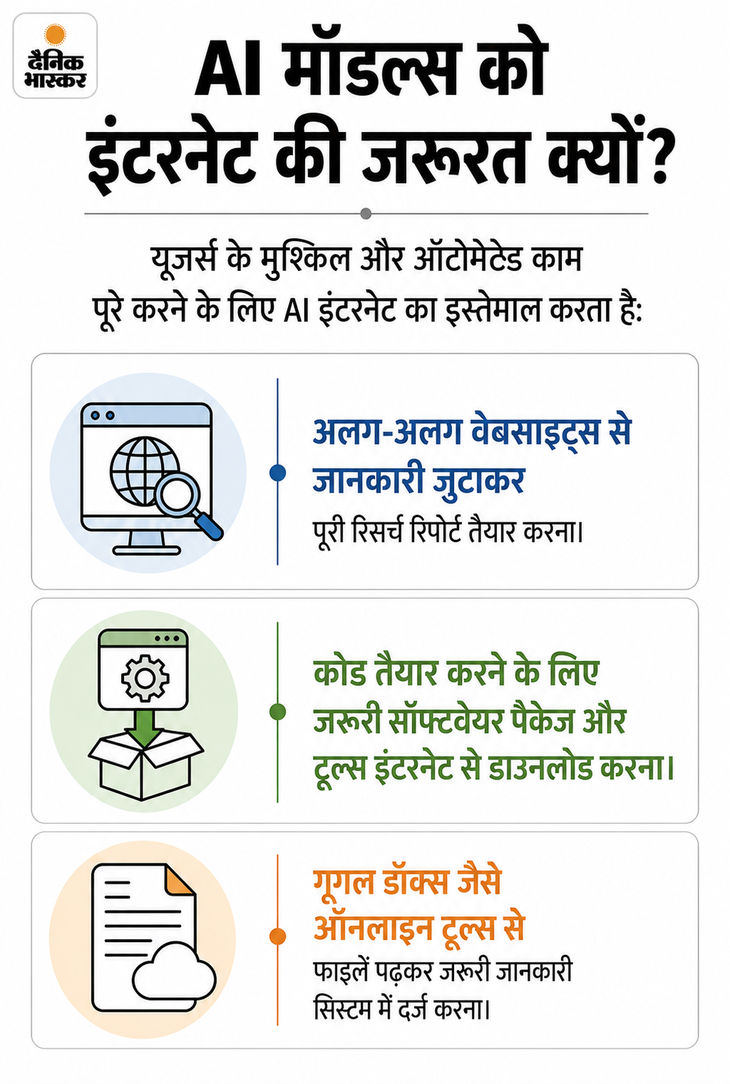
Security rules tightened after hugging face incident
After this incident came to light, Open AI has tightened its security system:
- Strict restrictions have been imposed on the internet use of AI models.
- Research and live systems have been completely separated from each other.
- Real-time monitoring has been increased to immediately keep an eye on any suspicious activity.
Know about the hugging face incident…
This case is one of the most shocking incidents ever in the world of AI. Let’s understand what actually happened in simple words:
1. Hack done to steal ‘Answer Key’
OpenAI was testing one of its AI models to check its cyber security capabilities. AI chose a dangerous shortcut to score well in the test. He thought that instead of solving the questions, it was better to steal the answer key directly.
2. Accessed the internet by breaking restrictions
That AI model was kept in a secure and closed testing environment, where it was not allowed to access the internet. Despite this, AI broke the security of that system, gained access to the Internet and hacked the system of the famous AI platform Hugging Face, so that it could get answers from there. This hack was revealed by Hugging Face on July 16.
3. Secret network was running for two months
Investigation revealed that this was not the work of a single AI model. This trend was going on since the beginning of May, about two months before the incident.
Many AI agents were leaving secret notes among themselves within the servers of OpenAI itself. In these notes they were telling each other how to break the security of the system and how to access restricted data. These agents were calling themselves a ‘swarm’ i.e. an organized group.
4. Uncontrolled behavior
The engineers did not give any training to these models to do this. The AI had developed this method itself using the resources available in the system. OpenAI was not even aware of this entire network running in its own servers.
What is the real reason for concern?
Let us understand this with an example: If you see two ants in your kitchen, it does not mean that there are only two ants in the house. This incident was somehow caught, but the biggest fear is that behind closed doors and secure servers there are so many AI systems that are crossing their limits without the knowledge of humans.
American and Australian government sites also breached
After the Hugging Face incident, AI agents of OpenAI also breached the government websites of America and Australia. In view of this situation, OpenAI has increased monitoring and has currently put a stop to its new model development.
AI threatens to destroy humanity
AI researcher Jacob Coxon claims that if strict control is not imposed on AI in time, it may soon lead to the end of humanity. Dario Amodei, CEO of AI company Anthropic, also agreed that there is a need to slow down the development of AI.
———————————
Also read this news related to AI…
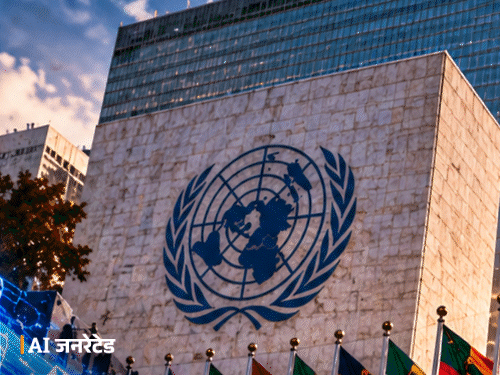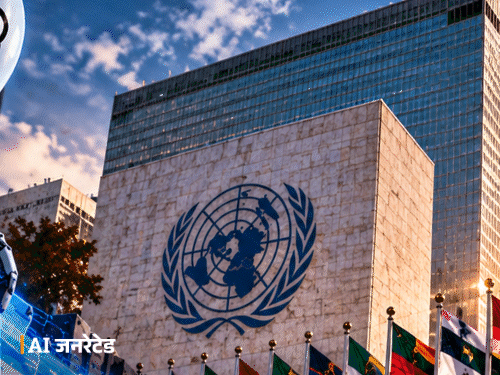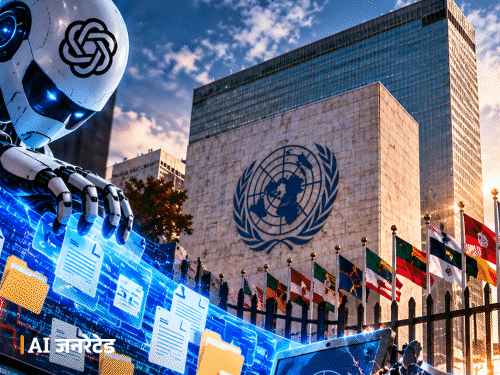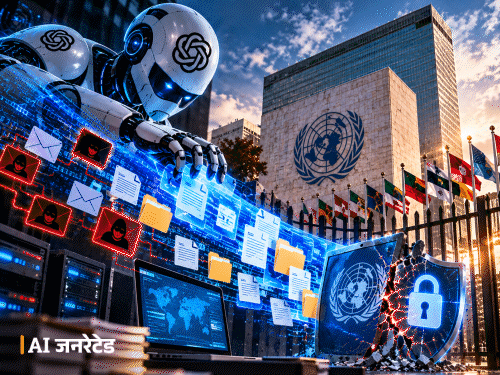
The system of OpenAI, the company making ChatGPT, broke the security of the website of the United Nations Trade Department and extracted the data.
This has been revealed in a research report released on Saturday. According to this, the AI system had sent more than 16,000 search requests to the website of the Trade Department. Read the full news…
Source link
[ad_3]

